About
A family business built on service
JKLO stands for Jennifer, Kyle, and Liam O'Neill. We're a veteran-owned, family business in rural Central Virginia, bringing enterprise-grade security experience to organizations of every size.
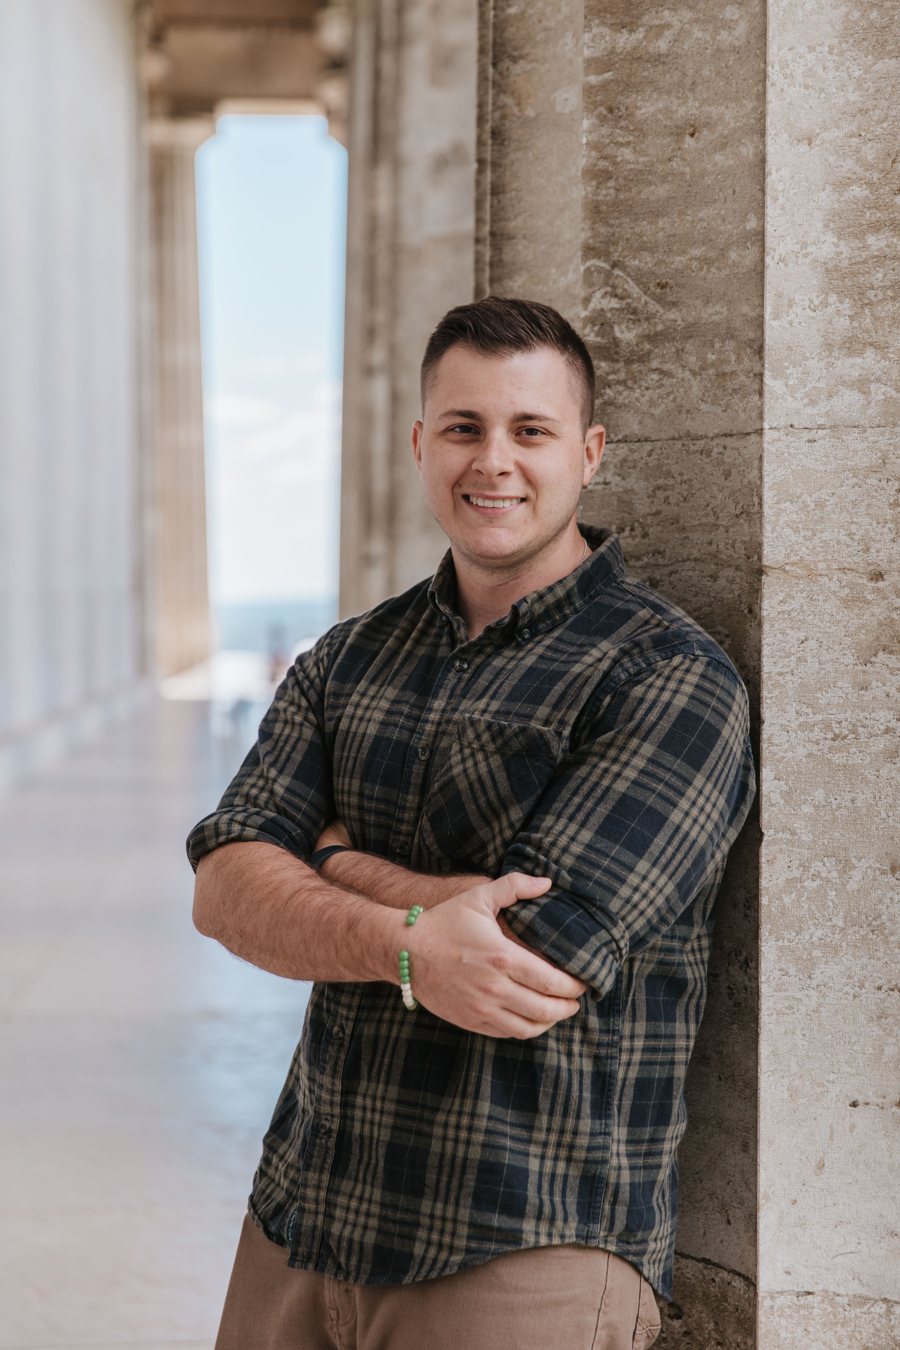
Principal consultant
Kyle O'Neill, CISSP
Kyle is a U.S. Army veteran and the principal consultant at JKLO Consulting. He brings more than a decade of experience in intelligence, security operations, and governance, risk, and compliance across the public and private sectors.
Kyle began his career in the Army as a signals intelligence analyst and Windows and Linux systems administrator, supporting joint operations and managing systems used for intelligence analysis. That experience shaped how he still approaches security today: understand the mission first, then protect what matters most to it.
After the Army, Kyle moved into cyber operations, leading analysts who hunted for threats across complex enterprise environments. He went on to lead a threat hunting and detection team that created and updated more than 300 detection rules aligned to the MITRE ATT&CK framework, and built a training program that helped analysts grow their careers and earn industry certifications, including the CISSP.
He then led security operations for a Fortune 100 customer and later managed a team of more than 17 security professionals providing 24/7/365 monitoring and incident response for multiple clients, while maintaining service-level adherence above 96%. In that role, he was the customer's primary contact during security incidents — the person who explained what happened, what it meant, and what to do next.
Today, Kyle focuses on governance, risk, and compliance. He leads internal and external security assessments against HITRUST, SOC 2, NIST SP 800-53, ISO 27001, and the CIS Controls; writes and maintains enterprise security policy; answers vendor and customer security questionnaires; and advises leadership on building security into projects from the start.
Kyle holds a Master of Science in Cybersecurity Management and Policy and a Bachelor of Science in Computer Networks and Cybersecurity from the University of Maryland Global Campus, along with the CISSP, SSCP, CompTIA CySA+, and Security+ certifications. He is currently pursuing the ISACA Certified Information Systems Auditor (CISA) certification.
Experience
From intelligence to security operations to GRC
More than a decade protecting systems and data across the public and private sectors.
- Today
GRC risk engineer
Leads internal and external assessments against HITRUST, SOC 2, NIST SP 800-53, ISO 27001, and CIS; writes enterprise security policy; answers third-party security questionnaires.
- 2024–2026
Security operations leadership
Led SOC teams for a Fortune 100 customer and a multi-client managed security provider — 17+ analysts, 24/7/365, >96% SLA adherence.
- 2020–2024
Threat hunting and cyber operations
Led analysts in threat hunting and incident response; built 300+ MITRE ATT&CK-aligned detections and a training program for new analysts.
- 2015–2021
U.S. Army
Signals intelligence analyst and Windows/Linux systems administrator supporting joint operations.
Certifications and education
- CISSP
- SSCP
- CompTIA CySA+
- CompTIA Security+
- Blue Team Level 1
- CISA (in progress)
- M.S. Cybersecurity Management & Policy
- B.S. Computer Networks & Cybersecurity
The family behind the name
Jennifer, Kyle, and Liam
JKLO Consulting is a family business. The name stands for Jennifer, Kyle, and Liam O'Neill. We live on a small farm in rural Central Virginia, where we raise poultry and other small livestock.
Farm life teaches you a few things that carry straight into security work: plan ahead, take care of the basics every single day, and don't cut corners on the things that keep everyone safe.
Kyle started JKLO to build a better life for his family — and to build something that lasts. After years of helping large organizations protect themselves, he saw how many small and mid-sized organizations were left out: too small for the big consulting firms, but facing the same customer demands, regulations, and threats.
JKLO exists to close that gap, with honest advice, practical plans, and the kind of personal service you'd expect from a family business.
What we believe
How we treat every client
Honesty first
We tell you what we find, even when it isn't what you hoped to hear. No fear tactics, and no selling you work you don't need.
Plain language
If your leadership can't understand the report, it isn't finished. We write for people, not auditors.
Practical over perfect
The best security plan is the one your team can actually carry out. We prioritize what makes the biggest difference first.
Your data, protected
We practice what we recommend: least-privilege access, encrypted communications, and careful handling of everything you share.
Let's talk
Whether you have a specific project or just a question, we'd be glad to hear from you.